
One sensor. Endpoint, network, identity. The browser next.
One lightweight agent captures endpoint, network and identity telemetry on the same device and sends it into one Data Fabric. No second agent, no SIEM to stitch it together.
<0.6%
CPU on Windows for endpoint plus network telemetry (docs.senseon.io)
~90 MB
Memory for endpoint plus network telemetry; about 300 MB with antimalware enabled
28 kbps
Steady-state bandwidth per host, around 300 MiB a day
0
Inbound ports. All communication is initiated from the endpoint over mutually authenticated TLS
Four telemetry domains, one device identity.
Because everything arrives with one device identity, a lure neutralised in the browser, the PowerShell it would have spawned, the beacon that would have followed and the sign-in that came after are one investigation, not four alerts in four consoles.

Endpoint
Process creation with parent and child relationships, hashes and signatures; file create, modify, delete and rename; authentication events; antimalware scan results where enabled. The same classes of event a traditional EDR agent records.

Network
TCP and UDP connections, DNS, TLS metadata and application-layer protocols, captured on the host and attributed to the process and user that generated them. For segments where no agent can run, a SenseOn network probe captures traffic at the switch.

Identity
User and authentication events from the endpoint, joined to identity-provider logs through the platform's integrations, so a credential warning and an unusual sign-in are one case.

Browser
Shadow AI data-leak verdicts and neutralised ClickFix lures from a managed browser extension, on the same device identity as the endpoint telemetry. Analysis on the device; only the verdict leaves.
One command. Intune, SCCM, GPO or NinjaOne. Alongside what you already run.
Installation is a single command per operating system, generated for your tenant inside the SenseOn platform. There is no key file to distribute.
Install in one command
New endpoints enrol with a secure token. The same command runs in PowerShell on one machine or across an estate through Intune, SCCM, Group Policy or NinjaOne. The sensor ships as one unified package that handles installation automatically.
Runs beside your EDR
The antimalware component has a dual-running mode designed to operate alongside another real-time scanner without interference. Add exclusions for SenseOn's install paths and processes in the other tool, deploy for visibility on day one, and decide about consolidation later.
Stays current, stays healthy
A background service keeps the sensor updated and monitors its health. Pin a version per device segment, choose the latest or previous release, and roll back if needed. Telemetry buffers on disk when a device is offline and uploads when it reconnects.
Configured centrally. Acts on the device.
Which capabilities are active is set from the platform, per segment, and pushed to the sensor. The sensor is also the platform's hand on the device.
Central configuration
Network analysis on or off; antimalware in scan-and-block, scan-only or dual-running mode; active response; automatic host isolation as a response action. The browser coverage will follow the same model: one build, behaviour set by server-delivered rules.
Active Response
Remote access to Windows and Linux endpoints and one-click isolation for analysts, from the same agent that collected the evidence.
Reflex host isolation
Automatic isolation of a compromised Windows device when a case reaches a threshold the customer sets. Investigation and response happen where the evidence was collected.
Supported platforms, and where the sensor sits
| Supported | Notes (from docs.senseon.io) | |
|---|---|---|
| Windows | Windows 8.1 and later desktop; Windows Server 2012 R2 and later | 64-bit and ARM. Minimum 2 GB RAM desktop, 512 MB Server Core; 4 GB recommended |
| macOS | Catalina 10.15 and later, Apple Silicon | Minimum 2 GB RAM; 4 GB recommended |
| Linux | Ubuntu 18.04+, Debian, CentOS/RHEL 7+ | x86_64. Kernel 5.2 or later (eBPF) for network telemetry; older kernels give process telemetry only |
| Browser | Managed Chrome, Manifest V3 | Deployed through your existing enterprise browser policy. Read more |
How it fits the platform
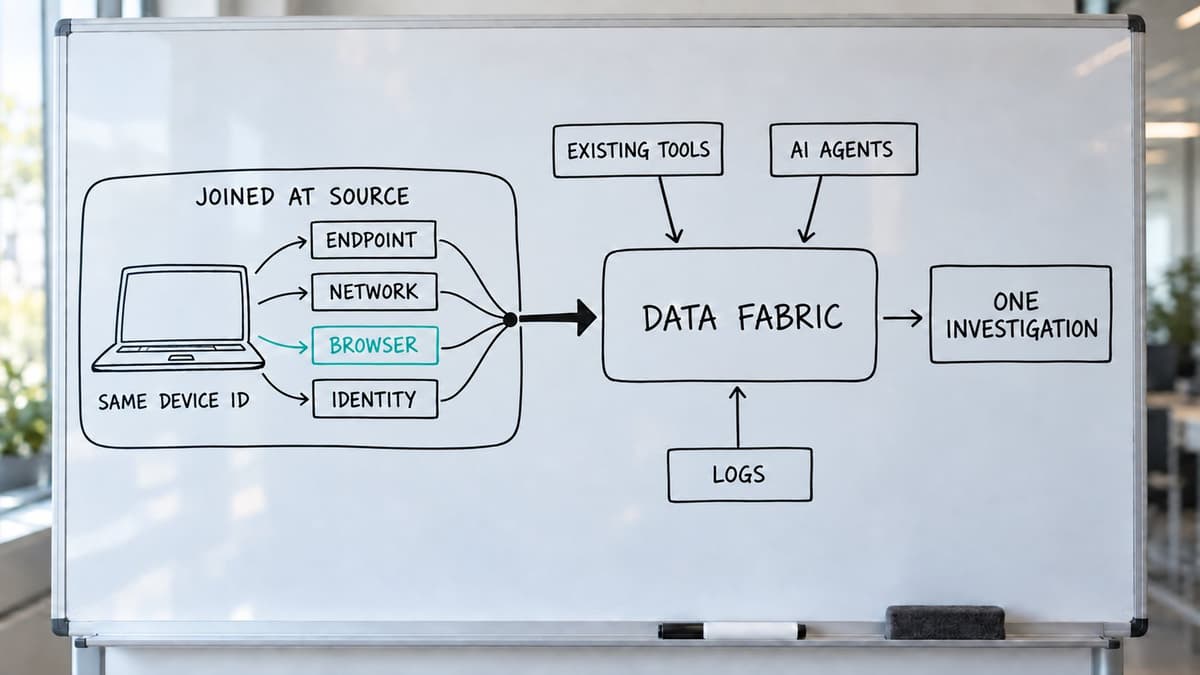
The Universal Sensor and network probes collect. Integrations bring identity, cloud, email, SaaS, vulnerability and AI-agent logs alongside. The Data Fabric unifies all of it, with edge processing compressing logs before they move. Built-in detection and correlation create cases. Horus and the specialist agents, Resolve among them, investigate and close them. One sensor at the start of that chain is why the platform can replace separate EDR, NDR, SIEM, SOAR and UEBA tools rather than integrate them. See how the sensor feeds the Intelligence Fabric.
What it does not do
From the docs: the sensor does not listen on any inbound port; all communication is initiated from the endpoint to your tenant's SenseOn domain over mutually authenticated TLS 1.2 or higher. Packet payloads are not transmitted to the platform. It does not capture keystrokes, read clipboard contents, or capture screen content. Telemetry is buffered on disk if the endpoint cannot reach the platform and uploaded when connectivity returns.
- Is the Universal Sensor an EDR agent?
- It does what an EDR agent does, capturing process, file, network and authentication telemetry and enabling isolation and remote response, and it also captures network flow metadata and identity events that EDR agents do not. That is why SenseOn describes itself as a unified detection and response platform rather than a traditional EDR.
- Can I run it alongside CrowdStrike, Defender or another EDR?
- Yes. Add exclusions for SenseOn's install locations and processes in the other tool, and set SenseOn's antimalware to dual-running mode if you keep another real-time scanner.
- Does it need a network appliance?
- No. Network analysis runs on the host, and network data is attributed to the process and user that generated it. A network probe is optional, for segments where no agent can be installed, such as OT or unmanaged devices.
- How much does it cost per device?
- SenseOn is priced as an annual pool of Flex Intelligence Credits with tiered plans, all on the pricing page. You pay for outcomes: detection and response across your data, analytics included, and the investigations our AI completes. Data volume is one meter, not the whole bill.
- Will it cover the browser?
- A managed browser extension will extend the sensor's coverage to shadow AI data leaks and ClickFix lures, analysing on the device and sending only verdicts.
Sensor facts on this page are documented on docs.senseon.io.

See one sensor replace four agents
Endpoint, network and identity today; the browser next. One install command, one Data Fabric, one investigation.